How To Xss
Modsecurity For Cwp Control Webpanel Wiki
In this xss tutorial i can give an explanation for the fundamentals of cross website scripting and the harm which could performed from an xss assault. many people treat an xss vulnerability as a low to medium hazard vulnerability, whilst in truth it is a harmful assault that could cause your users being compromised. embedding in xml; it’s hard to look how that api may want to do in any other case the launchpad integration code as a result uses tal code along these strains, the usage of the shape key-word to explicitly imply that the excerpts in question do not require html-escaping (like most excellent net frameworks, tal’s default is to break out all variable content material, so a success xss attacks on launchpad have historically been uncommon):
Xss what's pass-web site scripting? move-site scripting (also referred to as xss) is one of the most not unusual application-layer internet assaults. xss vulnerabilities goal scripts embedded in a web page which might be done on the client-facet (inside the person’s internet browser) in preference to at the server-facet. improvement on this put up, we will study a way to allow server-aspect caching in expressjs study on
redos vulnerabilities in npm spikes via 143% and xss continues to develop
snykio/ Xss vulnerabilities are common enough to have graced packages as large and famous as facebook, google, and paypal, and xss has been a mainstay on the owasp top 10 listing because its inception. xss vulnerabilities are particularly risky because an attacker exploiting an xss assault can gain the capacity to do regardless of the user can do, and to look. Go-web page scripting (xss) stays one of the maximum commonplace safety vulnerabilities currently discovered in net-packages. this article offers insight into how to test your programs for move-web site scripting (xss) defects the usage of each manual and automated method.
Cross-website online scripting wikipedia.
Go website online scripting (xss) is a common attack vector that injects malicious code into a prone internet software. xss differs from different internet assault vectors (e. g. sq. injections), in that it does no longer directly target the application itself. as an alternative, the customers of the web utility are those at. Move-website scripting (additionally referred to as xss) is one of the most common utility-layer internet attacks. xss vulnerabilities target scripts embedded in a web page which might be carried out on the patron-facet (within the user’s net browser) in preference to at the server-aspect.
A contemplated xss (or also known as a non-continual xss attack) is a selected type of xss whose malicious script bounces off of any other website to the sufferer’s browser. it's far passed how to xss within the query, commonly, in the url. it makes exploitation as clean as tricking a consumer to click on a hyperlink. Move-site scripting (xss) attacks are a type of injection, wherein malicious scripts are injected into in any other case benign and trusted web sites. xss assaults arise while an attacker uses an internet utility to ship malicious code, commonly inside the shape of a browser aspect script, to a specific give up consumer. Extra xss with the aid of jakob kallin and irene lobo valbuena is certified beneath a innovative commons attribution-sharealike three. zero unported license. the source code for extra xss is to be had on github. excess xss was created in 2013 as a part of the language-based totally protection route at chalmers university of era.
Movesite Scripting Xss Cheat Sheet Veracode
Move-web page scripting attacks (xss) may be utilized by attackers to undermine utility security how to xss in lots of methods. it's far most usually used to steal consultation cookies, which allows the attacker to impersonate the sufferer. similarly to that, xss vulnerabilities were used to create social networks worms, unfold malware, deface websites, and phish for credentials. Relying at the functionality and information processed with the aid of the susceptible software, xss vulnerabilities can pose a large hazard to the business. attackers should steal confidential information, perform unauthorized activities, and take over the complete web sessions of the sufferer users. the firewall can’t guard you from malware, xss and square-injection attacks modsecurity will help to enhance the security of your server and scripts you are the use of on it the way to speedy locate from ssh which rule id See extra motion pictures for the way to xss.

Go-website online scripting (xss) is a customer-side code injection assault. the attacker goals to execute malicious scripts in an internet browser of the sufferer by using consisting of malicious code in a valid web page or web software. the actual attack takes place whilst the sufferer visits the web web page or web application that executes the malicious code. To understand a way to save you cross-web site scripting (xss), see the thing entitled: “how to prevent cross-website scripting (xss)“. resources of untrusted input it is important which you do no longer forget capacity resources of untrusted input, as doing so may additionally imply you overlook a capability trouble.
The actual xss attack is formed through injecting unsanitised enter into an internet software. the enter is typically inside the form of javascript, that may be stored by the application and returned to different customers after they visit the web page. thereby executing the javascript within the customers browser. compliance how a huge rock discovered a tesla xss vulnerability jeremy kirk • july 16, 2019 compliance how to xss unexpected password pointers from nist mike wilson • july 15, 2019 ► compliance the way to defend ssh keys ► compliance constructing a framework for Cross website scripting prevention cheat sheet creation. this text offers a easy high quality model for stopping xss using output escaping/encoding well. while there are a huge variety of xss attack vectors, following a few easy guidelines can absolutely defend towards this critical assault.
Irongeek Com
Relying at the capability and statistics processed with the aid of the vulnerable utility, xss vulnerabilities can pose a huge danger to the commercial enterprise. attackers should steal exclusive facts, perform unauthorized sports, and take over the whole web periods of the victim customers. Cross-web site scripting (xss) is a kind of how to xss laptop security vulnerability typically determined in web packages. xss assaults permit attackers to inject patron-aspect scripts into net pages viewed by way of other customers. a go-website online scripting vulnerability may be used by attackers to skip get right of entry to controls including the equal-beginning policy. move-web site scripting executed on web sites accounted for roughly 84%.
Saved pass-site scripting. stored xss (additionally called chronic or 2nd-order xss) arises while an software receives information from an untrusted supply and consists of that statistics inside its later http responses in an hazardous manner.. the facts in query is probably submitted to the application through http requests; for instance, remarks on a blog put up, consumer nicknames in a talk room, or contact information on. Xss locator (polygot) the subsequent is a “polygot check xss payload. ” this test will execute in a couple of contexts which includes html, script how to xss string, js and url. Go-site scripting (xss) attacks are a form of injection, in which malicious scripts are injected into otherwise benign and depended on websites. xss attacks arise when an attacker makes use of a web software to send malicious code, normally inside the shape of a browser facet script, to a special stop consumer. insecure wep application please (oriwap) nancy snoke expertise xss christina mitchell social engineering at work the way to use effective have an impact on to benefit management purchase-in
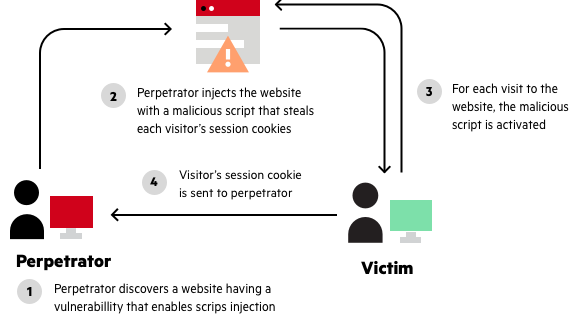
A entire guide to move website scripting (xss) assault, a way to prevent it, and xss testing. pass web page scripting (xss) is one of the most popular and susceptible assaults which is thought by every advanced tester. it's far taken into consideration as one of the riskiest assaults for the net programs and may convey dangerous effects too. may also 8, 2018 what's cross-web page scripting (xss) assault and the way to save you it muhammad haad ahmed june three, 2013


Komentar
Posting Komentar